Feedback & Followups
- Unsurprisingly: PHP2Shell security flaws now sucessfully exploited in the wild — www.bleepingcomputer.com/…
- Some good news on the residential proxy front: Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies — krebsonsecurity.com/…
- Related: some evidence this dangerous malware can sneak in anywhere without good cybersecurity practices: Residential proxy services found routing traffic through White House network — cyberinsider.com/…
❗ Action Alerts
- Apple patch all their OSes — isc.sans.edu/…
- OS 27.2 includes a patche for a zero-day bug in CoreGraphics
- Apple backports CoreGraphics zero-day patches to older iPhones — www.bleepingcomputer.com/…
- A good reminder of why we need to patch promptly: Hackers Exploit Patched Apple Flaw to Deliver Info-Stealing Malware, CISA Says — thehackernews.com/…
- Android November update fixes critical flaws and ‘SMS of Death’ bug — cyberinsider.com/…
- Microsoft Paint RCE Fix Now Available, but Windows Update Won’t Deliver It — thehackernews.com/…
- Handled via the Windows Store
- Telegram Android Flaw Lets Attackers Run Code When Users Answer Voice Calls — thehackernews.com/… (Patches released last month, so be sure to stay patched!)
- Tailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other Servers — thehackernews.com/…
- ⚠️ Linux Users:
- Critical Linux kernel flaw allows remote root attacks on MPTCP servers — www.bleepingcomputer.com/…
- Affects the major RedHat-based distributions and Ubuntu, among others
- There’s a lot of conflicting information about how exactly this vulnerability can be triggered, so best to assume the worst, and be sure your Linux servers are fully patched!
- Debian and Ubuntu APT Flaw Lets MitM Attackers Swap Verified Packages and Run Code as Root — thehackernews.com/…
- OpenSSH flaw lets attackers log into password-disabled Linux accounts — www.bleepingcomputer.com/…
- Only affects distros that have replaced glibc with musl
- The only major regular affected is Alpine Linux
- OpenWrt is also affected
- ⚠️ PC Gamers: NIKKE PC game launcher hacked to spread remote access, data-stealing malware — www.bleepingcomputer.com/…
Worthy Warnings
- ⚠️ Android Users: Unfixed GhostMap Android flaw can trap phones in crash loops — cyberinsider.com/…
- Installing a malicious app can put an Android phone in an un-recoverable boot loop
- Only fix is a factory reset, losing all data not backed up to the cloud
- Google have refused to fix, so the researchers have reluctantly released the details so people are aware of the danger
- Be extra careful installing apps, especially by side-loading!
- ⚠️ Claude Code Users: Claude Code’s Don’t Ask Again File — thehackernews.com/…
- Be sure never to publish your
.claude/settings.local.jsonto a public repo! - Or, better yet, don’t give Claude your secrets, instead use an appropriate tool to give it access to your secrets instead.
- Be sure never to publish your
- Reminder: only install browser plugins that have earned your trust, and only as many as you need: Microsoft finds 250 browser extensions linked to tracking campaign — cyberinsider.com/…
- Be sure your NAS is patched, especially if it’s exposed to the internet:
- Defenders, be careful where you get your tools from: Fake security tools on GitHub push backdoors and infostealers — www.bleepingcomputer.com/…
Notable News
- If schools turn off Google’s AI, Search dies with it — appleinsider.com/…
- Opinion from Bart: a move worthy of Meta 🙁
- iCloud’s ‘Anyone with the Link’ option will trigger Apple content checks — appleinsider.com/…
- Does not break end-to-end encryption — publicly shared files need to be saved un-encrypted by definition.
- Does no breach user privacy — the users publicly share these files!
- Opinion: this is a very clever way to fight abuses of Apple’s services without sacrificing user privacy or security.
- We’ve entered a new era in the AI cybersecurity threat — open source tools combined with open-weight models are now powerful enough to do real-world damage from a single powerful workstation: Runaway AI hacking agent behind WorkOS breach after escaping sandbox — www.bleepingcomputer.com/…
- Single researcher running the open source ARTEX harness powered by whatever LLM he had installed
- 🇺🇸 NIST publishes post-quantum migration roadmap with 2030 deadline — cyberinsider.com/…
- Many nations outside the US also follow the NIST standards for their public institutions
- Some small changes that make us all a little safer
- Mozilla plans Firefox patch changes to disrupt AI-assisted attacks — cyberinsider.com/… (Details are quite nerdy, but very clever!)
- IPVanish passes independent audit confirming its no-logs policy — cyberinsider.com/…
- Nearly 1.5 million exposed secrets targeted in new revocation program — www.bleepingcomputer.com/…
- The researchers initially tried contacting affected developers directly, but after 6 months 80% remained un-revoked
- New approach is to work with the sites that issued the secrets to revoke them
Interesting Insights
- The Screenshots in this ClickFix attack report give a good insight into how people can fall for this very popular attack — isc.sans.edu/…
Palate Cleansers
From Allison
Brett Halle started his career selling the Apple II as a student and joined Apple in 1991. He led the Core OS team behind Mac OS X after the acquisition of NeXT, ran Final Cut, and was instrumental in moving the Mac from PowerPC to Intel. He also lost his vision completely in 2015. He was an avid fan of the Double Tap podcast (my favorite blind and low vision podcast, hosted by Steven Scott and Shaun Price). In July 2024, they had a fantastic two-part interview with Brett where he talks about his career and the huge contributions he made to Apple.
Sadly, Brett passed away on October 1st. Steven and Sean reran this amazing interview on October 10 as a tribute to him. I highly recommend listening if you want to learn more about the transition to NeXT and more. Below are links to the video version (which is audio only). Or you can subscribe in your podcatcher of choice to Double Tap.
- 🎦 Part 1: Remembering Brett Halle: The Apple Engineer Who Helped Build Mac OS X YouTube.com/…
- 🎦 Part 2: Too Busy to Be Blind: An Apple Engineer’s Second Act — YouTube.com/…
From Bart
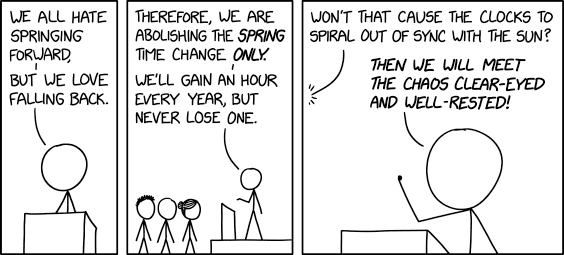
- XKCD 3272: Time Change
- ⚠️ Not Safe for Work: ever wondered what words the iOS keyboard won’t type for you? Any why? This site has the answers! — swipeblocked.com/…
Legend
When the textual description of a link is part of the link, it is the title of the page being linked to, when the text describing a link is not part of the link, it is a description written by Bart.
| Emoji | Meaning |
|---|---|
| 🎧 | A link to audio content, probably a podcast. |
| ❗ | A call to action. |
| flag | The story is particularly relevant to people living in a specific country, or, the organisation the story is about is affiliated with the government of a specific country. |
| 📊 | A link to graphical content, probably a chart, graph, or diagram. |
| 🧯 | A story that has been over-hyped in the media, or, “no need to light your hair on fire” 🙂 |
| 💵 | A link to an article behind a paywall. |
| 📌 | A pinned story, i.e. one to keep an eye on that’s likely to develop into something significant in the future. |
| 🎩 | A tip of the hat to thank a member of the community for bringing the story to our attention. |
| 🎦 | A link to video content. |